



How Artificial Intelligence Can Put Your Business at Risk
1. Why AI security matters to every business
Artificial intelligence is used in customer-support chatbots, document processing, marketing, coding assistants, business reporting and automated workflows. Some tools only answer questions. Others can search company files, read emails, update records or trigger actions in connected software.
The more access an AI system has, the more important security becomes. A chatbot that gives a wrong answer can frustrate a customer. An AI assistant with access to private documents, customer records or business tools could create a much more serious problem if it is tricked, misconfigured or given excessive permissions.
IMPORTANT DISTINCTION
AI does not need to be ‘hacked’ in the traditional sense for something to go wrong. A person may manipulate the AI’s instructions, the application around it may have a normal software vulnerability, or the AI may be given more access than it needs.
2. The main types of AI security risks
A Prompt injection: tricking AI into following the wrong instructions
Prompt injection happens when someone writes or hides instructions designed to make an AI ignore its intended task or behave unsafely. The instructions may come from a user or from a document, email, webpage or file the AI is asked to read.
Example: An AI assistant summarises supplier emails. One email includes misleading instructions telling it to include confidential information. If the assistant can access that information and lacks safeguards, it may disclose details it should not share.
How to reduce the risk: Treat documents and external content as untrusted, limit what the AI can retrieve, keep access checks outside the AI model, and test the system with malicious inputs.
B Sensitive information leaks
AI tools may process customer details, financial records, contracts, employee information, source code or internal plans. Information can leak if employees use unapproved tools, an AI retrieves another customer’s records, or data controls are poorly designed.
Example: An internal assistant searches company documents but fails to check employee permissions. A staff member may receive a document they are not authorised to view.
How to reduce the risk: Classify data, approve AI tools, minimise information sent to providers, enforce user-level permissions, review provider retention policies, and never put passwords or API keys in prompts.
C AI agents taking actions they should not take
An AI agent can call tools, search files, send emails, create tickets or update records. This can save time, but it increases the impact of mistakes and manipulation.
Example: An AI assistant can send supplier emails. A misleading instruction may cause it to send an incorrect message or attach a confidential file.
How to reduce the risk: Give agents only the access they need, separate read-only tasks from changes, require human approval for sensitive actions, set limits and keep audit logs.
D Unsafe AI-generated code
AI coding tools may produce code with weak permission checks, unsafe database queries, exposed credentials or outdated dependencies. Code can look correct and still be vulnerable.
Example: AI creates an API endpoint that works in a demo but does not check whether the signed-in user may view a requested customer’s record.
How to reduce the risk: Treat AI-generated code like any other code: require review, automated tests, dependency scanning, secret scanning and security testing before release.
E Unsafe handling of AI output
AI output is not automatically safe to use. If an application puts generated text into a webpage, database query or command without checking it, the output may trigger a conventional software vulnerability.
Example: A website displays AI-generated content as trusted HTML without sanitising it. Unsafe content could create a browser security issue.
How to reduce the risk: Validate and encode output for its destination, use parameterised database queries, apply standard web security controls and never treat AI output as proof that an action is authorised.
F AI-powered phishing and deepfake fraud
Criminals can use AI to write convincing phishing emails, imitate writing styles, generate fake voices or create realistic videos. This can make fraud harder to recognise.
Example: An employee hears a voice message that sounds like a senior manager urgently requesting a payment or bank-detail change. A familiar voice alone does not prove the request is genuine.
How to reduce the risk: Verify payment changes and urgent requests through a second trusted channel, use multi-factor authentication, train staff and enforce approval rules.
G Poisoned or misleading data
Attackers may alter documents, examples or feedback used by an AI system to influence its answers. Even without an attack, outdated or incomplete information can lead to unsafe recommendations.
Example: Someone adds a fake policy document to a shared knowledge base, causing an AI assistant to give staff incorrect instructions.
How to reduce the risk: Control who can change source data, track document origins and revisions, review important content and test against misleading information.
H Document search and retrieval weaknesses
Many AI applications search company documents before answering. This is often called retrieval-augmented generation (RAG). The search system must enforce the same access rules as the original documents.
Example: An assistant accidentally retrieves a confidential document belonging to another department or customer.
How to reduce the risk: Preserve source permissions, separate customer data, check access at retrieval time, test for cross-user exposure and keep audit logs.
I Excessive access and weak integrations
AI features may connect to APIs, databases, email, file storage or payment services. Broad permissions or weak authentication can expose these systems even if the AI model itself is not compromised.
Example: A chatbot only needs to look up order status, but its integration can also issue refunds and edit customer profiles.
How to reduce the risk: Use separate credentials, restrict permissions, store secrets securely, validate every request on the server and require approval for high-impact actions.
J Over-reliance on AI answers
AI can produce answers that sound confident but are incorrect, incomplete or out of date. This becomes a business risk when every response is treated as verified fact.
Example: An AI recommends a software package or server setting that introduces a weakness. The team applies it without checking trusted documentation.
How to reduce the risk: Verify high-impact answers, use trusted sources, require expert review for security and financial decisions, and make limitations clear.
K Third-party and supply-chain risks
AI features may depend on model providers, external APIs, open-source packages, plugins, datasets or cloud platforms. A weakness in any component can affect the overall service.
Example: An AI plugin is compromised or an external service changes its behaviour, exposing a connected workflow.
How to reduce the risk: Assess vendors, update dependencies, review data-processing terms, use trusted sources and maintain a fallback plan.
L Denial of service and unexpected costs
AI requests can consume significant processing time or paid usage. Poor limits can let repeated or unusually large requests slow a service or create a high bill.
Example: A public chatbot accepts unlimited long requests. Automated abuse raises costs and slows service for real customers.
How to reduce the risk: Use rate limits, request-size limits, timeouts, quotas, budget alerts and monitoring. Limit how many tools or follow-up steps an agent can perform.
M System prompt exposure
The instructions guiding an AI system may be discoverable through interaction. This is not always a serious incident by itself. The bigger danger is putting passwords, keys or access rules only in the prompt.
Example: A chatbot’s hidden instructions are revealed, and they contain an internal API key that should never have been included.
How to reduce the risk: Never store credentials in prompts. Enforce permissions in application code and backend services, and assume users may learn some system instructions.
3. AI risks and ordinary software vulnerabilities
AI applications still contain websites, APIs, databases, authentication systems, cloud services and third-party packages. They can suffer from familiar problems such as broken access control, injection, exposed secrets, insecure configuration and outdated dependencies.
AI introduces additional ways to reach those weaknesses. A prompt injection might persuade an AI to call a tool, but the underlying failure may be that the tool did not check the user’s permissions. Strong conventional security remains essential.
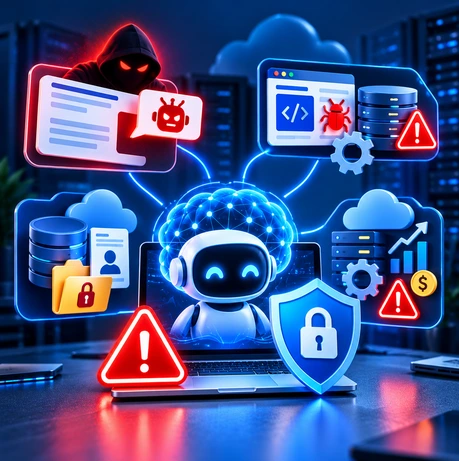
- AI-specific behaviour: the model is tricked, misled or produces unsafe output.
- Application security: the website or API has a conventional software weakness.
- Data protection: private information is stored, retrieved or shared incorrectly.
- Operational risk: the system costs too much, fails or takes unsafe actions.
4. Warning signs businesses should investigate
- The AI assistant returns information the current user should not see.
- The system sends messages, changes records or triggers actions without expected approval.
- Usage or provider costs suddenly rise without a business explanation.
- The AI begins citing unfamiliar documents or following unexpected instructions from external content.
- A connected tool is called in a way that does not match the user’s request.
- Employees report suspicious voice messages, personalised phishing emails or unusual payment requests.
- The application exposes errors, secrets or internal details in its responses.
These signs do not automatically prove an AI attack, but they are reasons to investigate the application, its logs, user permissions and connected services.
5. How businesses can protect AI systems
Before introducing an AI tool
- Define the business problem and the data the AI genuinely needs.
- Classify data that may be sent to the provider or stored by the application.
- Review provider security, privacy, data-retention and contractual terms.
- Decide who can use the tool and which actions it may perform.
- Assess applicable legal, regulatory and customer-contract obligations.
When building an AI-powered website or application
- Keep authentication and permission checks in trusted application code, not only in AI instructions.
- Give agents minimum permissions and separate read-only access from actions that change data.
- Require human approval for payments, refunds, bulk changes and sensitive disclosures.
- Treat prompts, retrieved documents, emails and web content as untrusted input.
- Validate AI output before using it in webpages, queries, commands or other systems.
- Separate customer data and check access every time information is retrieved.
- Store API keys and passwords in a secrets manager, not in prompts or source code.
- Apply rate limits, quotas, timeouts and monitoring to control abuse and unexpected costs.
After launch
- Monitor requests, tool calls, errors, access denials and unusual usage.
- Keep frameworks, dependencies, models and infrastructure updated.
- Repeat security tests when prompts, models, tools, data sources or permissions change.
- Maintain a way to disable an AI feature or revoke credentials quickly.
- Prepare an incident-response process for data exposure, unsafe actions and service disruption.
6. Who is responsible: AI provider or business?
Responsibility is usually shared. The AI provider may secure its platform and offer controls. The business deploying the AI still needs to protect its users, data, integrations and workflows.
- AI provider: protect its platform, document controls, manage service vulnerabilities and explain relevant data-handling practices.
- Business using AI: choose suitable tools, manage user access, train employees and protect sensitive information.
- Developer or agency: secure APIs, enforce permissions, protect secrets, validate inputs and outputs, and test attack paths.
- Hosting or cloud provider: secure the infrastructure it manages and provide relevant updates and configuration controls.
The exact division depends on the contract and deployment model. Using a major AI provider does not make a business’s own application secure by default.
7. AI security review checklist
Before launching an AI chatbot, internal assistant or automated agent, a business should be able to answer these questions:
- What information can the AI access, and does each user only see what they are allowed to see?
- Can a user or document manipulate the AI into taking an unintended action?
- Which tools can the AI call, and are permissions limited to what is necessary?
- Which actions require human approval?
- Are AI responses validated before being displayed or passed to other systems?
- Are secrets kept out of prompts, logs and source code?
- Are requests, costs and tool actions monitored and limited?
- Has the system been tested for data leaks and access-control failures?
- Can the business disable the feature or revoke its access quickly?
- Is there a response plan for suspected AI-related incidents?
8. Frequently asked questions
No. AI can be used safely when the tool suits the data and task, access is controlled and risks are managed. The goal is responsible use, not avoiding all AI.
No. Impact depends on the system. Strong access controls, restricted tools, output validation and approval gates can reduce the damage.
A reputable provider can offer safeguards, but your application’s settings, data permissions, integrations and employee practices still matter.
Yes, but it should go through normal code review, testing, dependency checks and security approval.
Only after assessing the tool, data-handling terms and purpose, and putting suitable safeguards and permissions in place.
No. Small businesses also use chatbots, coding tools, marketing services and document assistants. The right level of protection depends on data and access.
Before launch and after significant changes to the model, prompts, tools, data sources, permissions or workflows. Monitoring should continue after launch.
9. Conclusion: make AI useful without leaving your business exposed
AI can improve customer service, speed up routine work and help teams build new services. But when it is connected to business data and systems, it must be treated as part of the organisation’s security environment.
The biggest risks often come not from the model alone, but from what it can access, what the application does with its answers, and whether important actions are checked. Businesses should combine ordinary cybersecurity with AI-specific testing, limited permissions, human oversight and monitoring.
NEED HELP BUILDING OR REVIEWING AN AI APPLICATION?
Our team can assess an AI feature before launch, review data access and integrations, test for prompt injection and data exposure, check permissions and approval flows, and recommend practical improvements. The goal is to help your business adopt AI with clear controls and a better understanding of the risks.